

 Lavkush
MySQLi and PDO are the two main ways PHP talks to a MySQL database. MySQLi works only with MySQL and feels a little simpler at first, while PDO works with many database systems, uses named placeholders in queries, and is the safer long-term choice for most new projects. In this guide you will see the exact same tasks written both ways, so the difference stops being theory and becomes obvious.
Every PHP beginner reaches this fork in the road. One tutorial uses mysqli_connect(), the next one uses new PDO(), and both claim to be "the right way". The good news: neither is wrong. The better news: once you understand what each one is good at, picking between them takes about ten seconds.
What MySQLi and PDO Actually Are
MySQLi stands for "MySQL Improved". It is a PHP extension built specifically for MySQL databases. It gives you two styles of writing code: a procedural style with functions like mysqli_query(), and an object-oriented style with classes like mysqli. The official MySQLi book in the PHP manual documents both styles side by side, which is handy when old tutorials mix them.
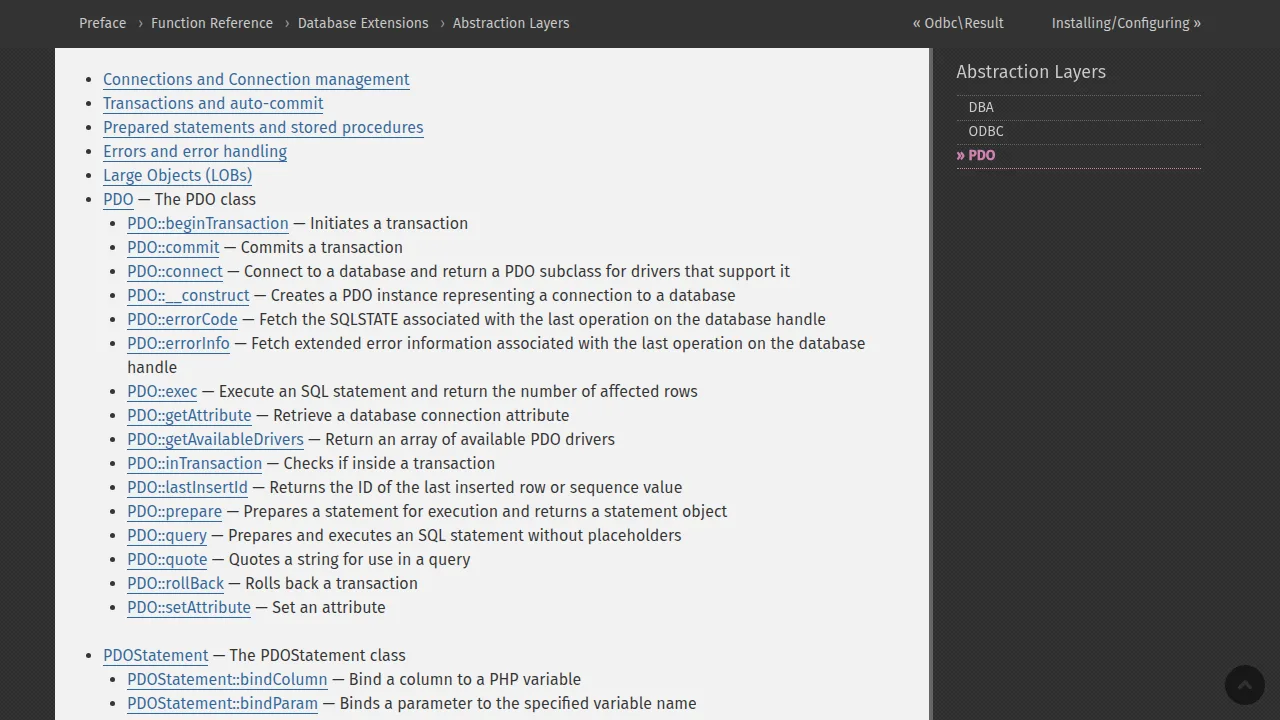
PDO stands for "PHP Data Objects". Instead of being tied to one database, PDO is a consistent layer that works with MySQL, PostgreSQL, SQLite and several others through small driver modules. You learn one set of methods, and the PDO book in the PHP manual shows how the same code shape works across all of them. Think of MySQLi as a specialist and PDO as a well-trained generalist.
Connecting to the Database: Side by Side
Let us start where every script starts: the connection. Here is MySQLi in its object-oriented style:
$mysqli = new mysqli("localhost", "root", "", "school");

if ($mysqli->connect_error) {
    die("Connection failed: " . $mysqli->connect_error);
}
echo "Connected with MySQLi";
And here is the same connection with PDO:
try {
    $pdo = new PDO("mysql:host=localhost;dbname=school", "root", "");
    $pdo->setAttribute(PDO::ATTR_ERRMODE, PDO::ERRMODE_EXCEPTION);
    echo "Connected with PDO";
} catch (PDOException $e) {
    die("Connection failed: " . $e->getMessage());
}
Two differences jump out. First, PDO packs the database type, host and database name into one connection string called a DSN. Second, PDO uses exceptions for errors, so a failed connection lands neatly in a catch block instead of needing a manual check after every step. If connecting is still new to you, our beginner guide on how to connect PHP with a MySQL database walks through the setup slowly before you compare the two styles.
Running the Same Query Both Ways
Now the part that matters daily: reading rows safely with a prepared statement. Prepared statements separate the SQL shape from the values, which is what protects you from SQL injection. Here is a lookup by student ID in MySQLi:
$stmt = $mysqli->prepare("SELECT name, marks FROM students WHERE id = ?");
$stmt->bind_param("i", $id);
$id = 3;
$stmt->execute();
$result = $stmt->get_result();
$row = $result->fetch_assoc();
echo $row["name"] . " scored " . $row["marks"];
And the same lookup in PDO:
$stmt = $pdo->prepare("SELECT name, marks FROM students WHERE id = :id");
$stmt->execute(["id" => 3]);
$row = $stmt->fetch(PDO::FETCH_ASSOC);
echo $row["name"] . " scored " . $row["marks"];
Both are safe. But notice the PDO version: the placeholder has a name (:id), and the values go in as one tidy array inside execute(). MySQLi makes you call bind_param() with a type string like "i" for integer or "s" for string, and the order of variables must match the order of question marks exactly. It works fine — it is just easier to trip over when a query grows to eight or ten values. We have all bound them in the wrong order at least once. It builds character, apparently.
Inserting a Row: One More Comparison
Reading data is only half of daily work, so here is one insert each way. MySQLi first:
$stmt = $mysqli->prepare("INSERT INTO students (name, marks) VALUES (?, ?)");
$stmt->bind_param("si", $name, $marks);
$name = "Asha";
$marks = 91;
$stmt->execute();
echo "Saved with MySQLi, new ID: " . $stmt->insert_id;
And PDO:
$stmt = $pdo->prepare("INSERT INTO students (name, marks) VALUES (:name, :marks)");
$stmt->execute(["name" => "Asha", "marks" => 91]);
echo "Saved with PDO, new ID: " . $pdo->lastInsertId();
The pattern repeats: MySQLi needs the extra bind_param() line with its type letters in exactly the right order, while PDO reads almost like a labelled form — each value arrives with its name attached. Neither version is hard, but across a whole project with dozens of queries, the PDO style quietly saves time and prevents a whole category of silly ordering mistakes.
MySQLi vs PDO: The Full Comparison Table
| Feature | MySQLi | PDO |
|---|---|---|
| Databases supported | MySQL only | MySQL, PostgreSQL, SQLite and more |
| Code style | Procedural and object-oriented | Object-oriented only |
| Placeholders | Question marks (?) only | Question marks and named placeholders (:name) |
| Binding values | bind_param() with a type string | Values passed as an array to execute() |
| Error handling | Error codes and warnings by default | Exceptions when error mode is set |
| Switching database later | Rewrite the data layer | Change the DSN and minor details |
| Extra MySQL features | Full access to MySQL-specific options | Covers common features; a few MySQL-only extras differ |
The table hides one honest point in MySQLi's favour: because it is MySQL-only, it exposes a few MySQL-specific features directly, and its procedural style can feel gentler on day one if you have not learned classes yet. PDO asks you to be comfortable with objects and exceptions from the start — a small hill that pays off quickly.
Which One Should You Actually Use?
For most beginners building new PHP and MySQL projects today, PDO is the recommended default. Named placeholders keep big queries readable, exceptions make error handling cleaner, and if your project ever moves from MySQL to PostgreSQL or needs a quick SQLite file for testing, your data code mostly survives the move. Frameworks agree with this direction too: modern PHP tools are built around PDO-style database access.
MySQLi is still a perfectly reasonable choice when you know the project will stay on MySQL forever, when you are maintaining older code that already uses it, or when a course or exam expects it. Plenty of production sites run on MySQLi happily. The real mistake is not picking the "wrong" one — it is mixing both randomly in the same project, or skipping prepared statements altogether. Pick one, use prepared statements everywhere, and your database code will be in good shape.
A practical way to feel the difference is to build something small with each. Our step-by-step project to build a simple CRUD app in PHP and MySQL gives you adding, viewing, editing and deleting records — try following it once with PDO, and you will see exactly where the named placeholders save you effort.
Frequently Asked Questions
Is PDO slower than MySQLi?
In everyday projects, no difference you can feel. Both sit on fast native drivers, and your queries and indexes affect speed far more than the extension you choose.
Can I use MySQLi and PDO in the same project?
Technically yes, but please do not. Mixing them makes code confusing to read and maintain. Choose one style per project and stay consistent.
Which one is safer against SQL injection?
Both are equally safe when you use prepared statements properly. The danger comes from gluing user input directly into query strings, and that mistake is possible — and equally bad — in both.
I am learning PHP for an exam. Which should I learn first?
Learn PDO first if you have a choice, because its style transfers to other databases and frameworks. But check your syllabus: many college courses still teach MySQLi, and matching your course saves exam-day stress.
Conclusion
MySQLi is the MySQL specialist: simple, direct, and fine for MySQL-only work. PDO is the flexible all-rounder: named placeholders, exception-based errors, and freedom to change databases later. For a new project in 2026, start with PDO, write every query as a prepared statement, and you will rarely need to think about this choice again.
Leave a Comment